NIS2 · GOVERNANCE
“We implemented it” is not yet evidence.
NIS2 makes information security an organisational and leadership matter too. Ownership, implementation and evidence need to fit together.
Austria in focus, with DACH context. Not legal advice.
NISG 2026 · AUSTRIA
01.10.2026
enters into force
IN PRACTICE
Sooner or later, someone will ask to see it.
“Yes, of course we documented that.”
“Hang on, I think it should be in here somewhere.”
WHERE IS IT?
- Open the spreadsheet.
- Search SharePoint.
- Ask a colleague.
- Open another spreadsheet.
This is where NIS2 becomes an organisational question.
Who owns it? What has been done? What proves it?
- Requirement
- Owner
- Measure
- Evidence
- Status
Germany: implementation law in force since 6 December 2025. Switzerland: a separate reporting regime outside the EU NIS2 framework.
REPORTACT · NIS2
Stop starting every framework from scratch.
NIS2, DORA, ISO 27001, GDPR, the EU AI Act, the CRA … the list is not getting shorter. What I like about ReportAct is the simple idea behind it: bring requirements together, reuse the controls and evidence you already have, and stop reorganising the same work for every new framework.
When someone asks for evidence, “my colleague should have that” probably shouldn’t be your first line of defence.
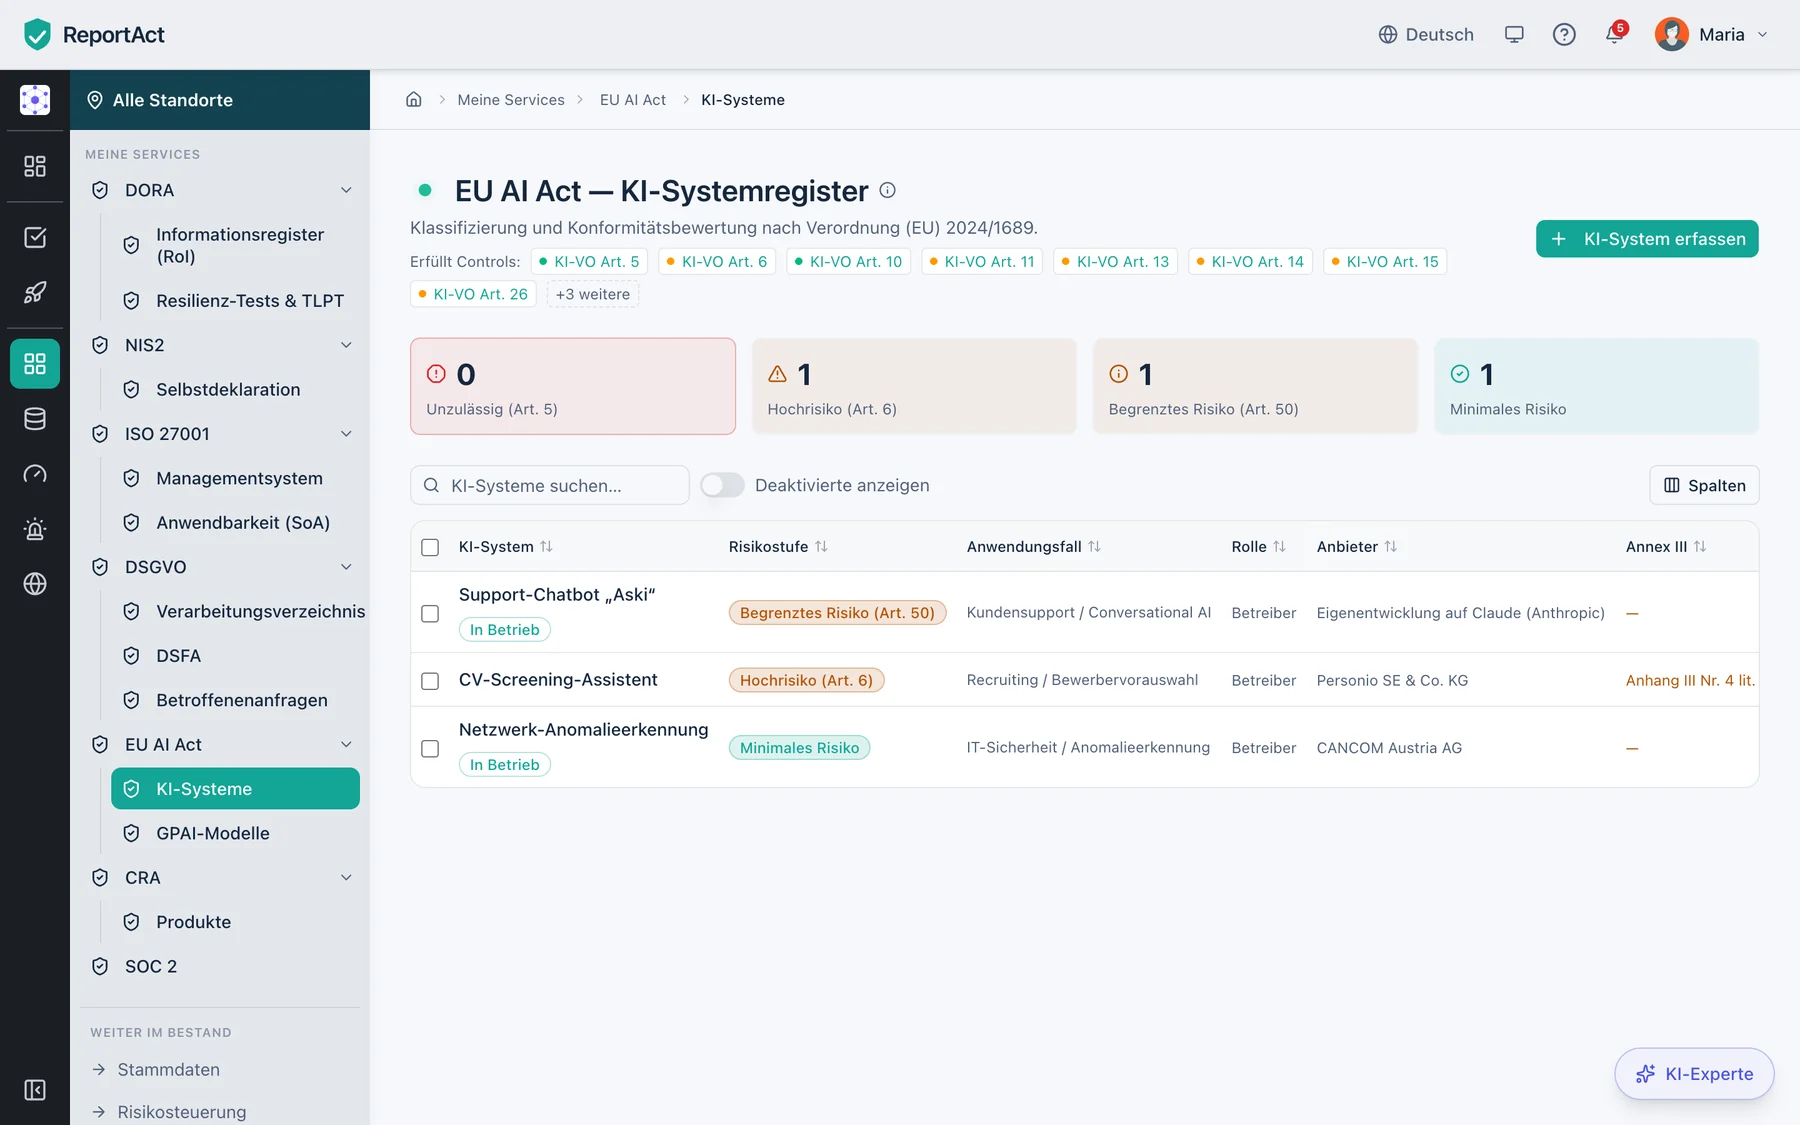
It still won’t make compliance sexy. But at least you’ll find the spreadsheet.